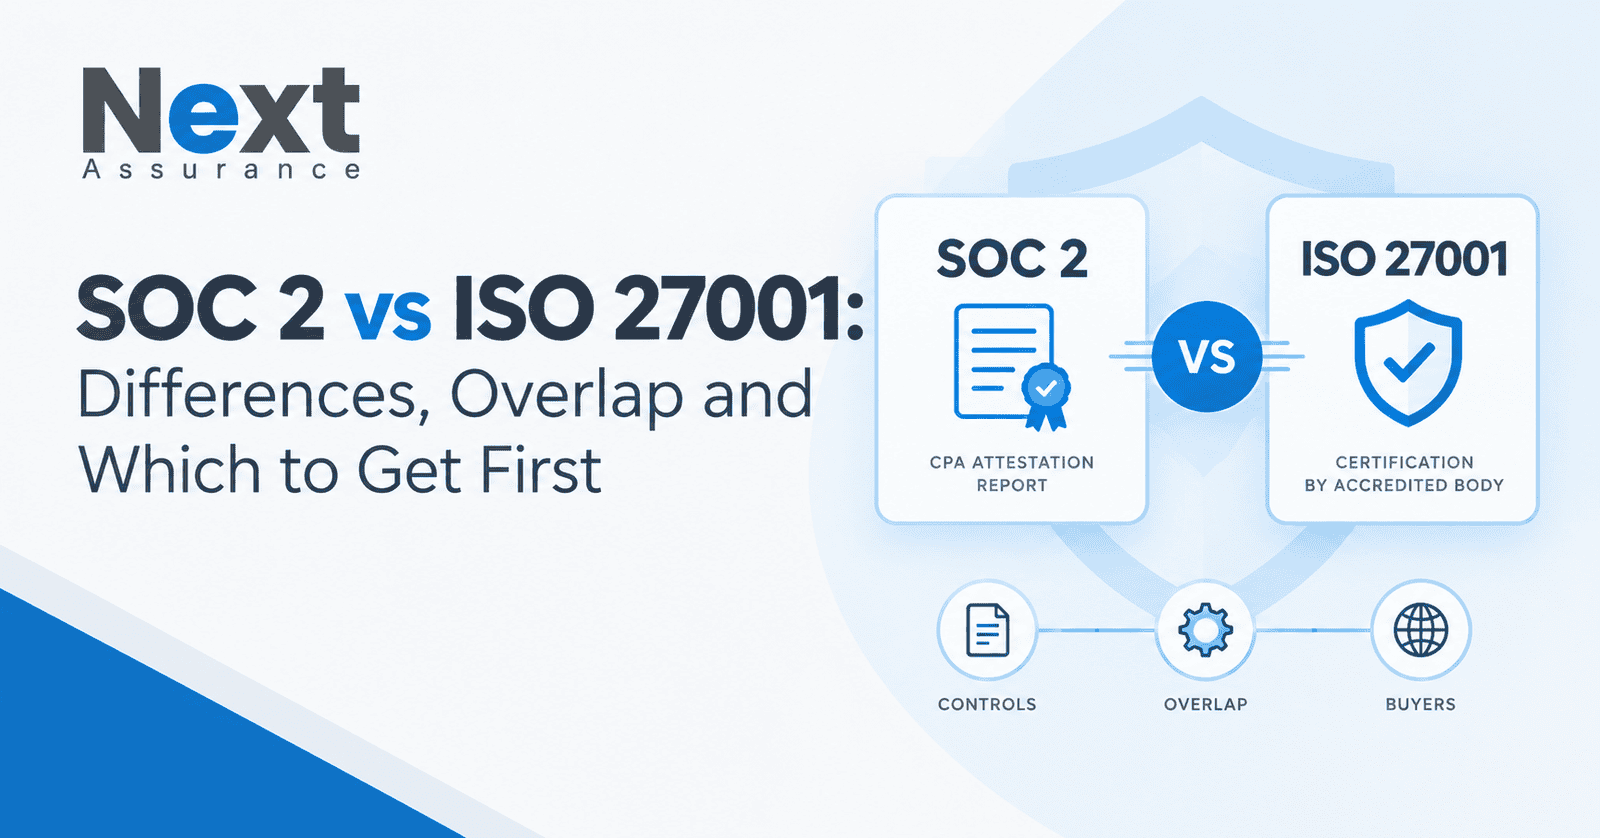
SOC 2 is an attestation report issued by a CPA firm against the AICPA’s Trust Services Criteria, while ISO/IEC 27001 is an international standard for an information security management system (ISMS) that an accredited certification body can certify. They overlap heavily in controls but differ in who audits, what you receive and which buyers recognize it.
What is the difference between SOC 2 and ISO 27001?
The main difference is the form of assurance. SOC 2 is a report from a licensed CPA firm describing your controls and the tests performed, while ISO 27001 is a certification that your information security management system meets the standard’s requirements.
| Aspect | SOC 2 | ISO/IEC 27001 |
|---|---|---|
| Issued by | Licensed CPA firm under AICPA standards | Accredited certification body, against an ISO standard |
| Output | Detailed report with opinion, system description and test results | Certificate of conformity to the ISMS standard |
| Basis | AICPA Trust Services Criteria | ISMS requirements plus Annex A controls |
| Control selection | Management designs controls to meet the selected criteria | Organization selects controls from Annex A based on risk |
| Is it mandatory? | No; customers ask for it | No; certification is optional |
| Distribution | Restricted use, usually under NDA | Certificate can be shared widely |
ISO states that organizations implementing ISO/IEC 27001 can decide whether to go through certification at all. For the SOC side, see our SOC 2 audit guide.
What is ISO/IEC 27001:2022 and what changed?
ISO/IEC 27001:2022 is the third edition of the ISO standard for information security management systems, published in October 2022. It replaced the 2013 edition, which ISO now lists as withdrawn.
The 2022 edition restructured Annex A to 93 controls, down from 114 in 2013, according to the Cloud Security Alliance. The International Accreditation Forum set the certificate transition deadline at October 31, 2025 (IAF MD 26), so a current certificate should be to the 2022 edition. ISO also asks that the standard be cited in full, for example “certified to ISO/IEC 27001:2022.”
Which controls do SOC 2 and ISO 27001 share?
SOC 2 and ISO 27001 share most of the control areas that matter for a technology company: risk assessment, access control, change management, incident response, logging, vendor management and business continuity. The same policy and the same evidence often serve both.
- Access control: provisioning, reviews, MFA and removal for leavers.
- Risk management: a documented, periodic risk assessment.
- Operations: logging, monitoring, vulnerability management and change control.
- Resilience: backup, recovery and continuity planning.
- Supplier management: due diligence on the vendors you rely on.
What differs is structure. ISO 27001 requires a management system with a defined scope, leadership commitment and continual improvement, while SOC 2 tests the criteria you select. Our Trust Services Criteria guide lists the SOC 2 categories.
Which should a U.S. company get first?
Most U.S. SaaS companies get SOC 2 first, because U.S. enterprise procurement teams commonly ask for it by name. Get ISO 27001 first, or alongside, when your customers are outside the United States or your contracts name it.
| Your situation | Usual starting point |
|---|---|
| Selling mainly to U.S. enterprises | SOC 2 (Type II when buyers expect it) |
| Selling in Europe, Asia or to multinationals | ISO/IEC 27001:2022, often plus SOC 2 |
| Contract or RFP names one framework | The one named |
| Both regions | Build one control set, then pursue both |
This reflects common buyer practice rather than a sourced statistic; check what your own prospects require.
Can you reuse work for both?
Yes. Because the control areas overlap, a company that has done one can usually reach the other with less effort than starting from zero. Reuse is strongest for policies, access reviews, change records and vendor assessments.
Plan the control set once, map each control to both frameworks, and collect evidence once. Expect extra work specific to each: the ISMS documentation and Annex A selection for ISO, and the system description and operating-period testing for SOC 2. A compliance automation platform can map one set of evidence to several frameworks. For a U.S. framework comparison, see SOC 2 vs NIST CSF 2.0.
Next Assurance helps you choose the report that your buyers actually ask for and scope it once. See our SOC 2 audit service.
Frequently asked questions about SOC 2 vs ISO 27001
What is the main difference between SOC 2 and ISO 27001?
SOC 2 is an attestation report where a licensed CPA firm tests your controls against the AICPA Trust Services Criteria and issues an opinion. ISO 27001 is a standard for an information security management system, and an accredited certification body can certify conformity. One gives you a detailed report; the other gives you a certificate.
Do I need both SOC 2 and ISO 27001?
Not necessarily. Choose based on who buys from you. U.S. enterprise customers commonly ask for SOC 2, while international customers often ask for ISO 27001. If you sell in both markets, pursue one control set and certify or attest to both, since most control areas and evidence overlap.
Is ISO 27001 certification mandatory?
No. ISO states that organizations implementing ISO/IEC 27001 can decide whether they want to go through a certification process. Some certify to reassure customers, while others adopt the standard only for its practices. A certificate from an accredited body adds confidence because the accreditation body has confirmed the certifier’s competence.
Which version of ISO 27001 is current?
ISO/IEC 27001:2022, the third edition, published in October 2022. The 2013 edition and its corrigenda are listed as withdrawn, and the certificate transition deadline set by the International Accreditation Forum was October 31, 2025. Ask your certification body to confirm that any certificate you rely on references the 2022 edition.
Which is harder to get, SOC 2 or ISO 27001?
Neither is universally harder; they demand different work. ISO 27001 requires a documented management system, a defined scope and Annex A control selection. SOC 2 requires designing controls for the chosen criteria and, for Type II, proving they operated over a period. Your starting maturity matters more than the framework.
Can one audit cover both SOC 2 and ISO 27001?
They are separate engagements with different bodies: a CPA firm for SOC 2 and an accredited certification body for ISO 27001. You can share the same policies and evidence, and some firms coordinate timelines, but each produces its own report or certificate, with its own scope and opinion or decision.
Sources
Facts checked against primary sources on October 7, 2026.
- ISO – ISO/IEC 27001:2022 Information security management systems: edition and publication date; the 2013 edition is withdrawn.
- ISO – ISO/IEC 27001 information security management: organizations decide whether to certify; accredited certification adds confidence.
- Cloud Security Alliance – How to prepare for ISO/IEC 27001:2022: 93 Annex A controls versus 114 in 2013; transition deadline of October 31, 2025 under IAF MD 26.
- AICPA & CIMA – System and Organization Controls: SOC Suite of Services: the AICPA’s overview of SOC 1, SOC 2 and SOC 3 reports.