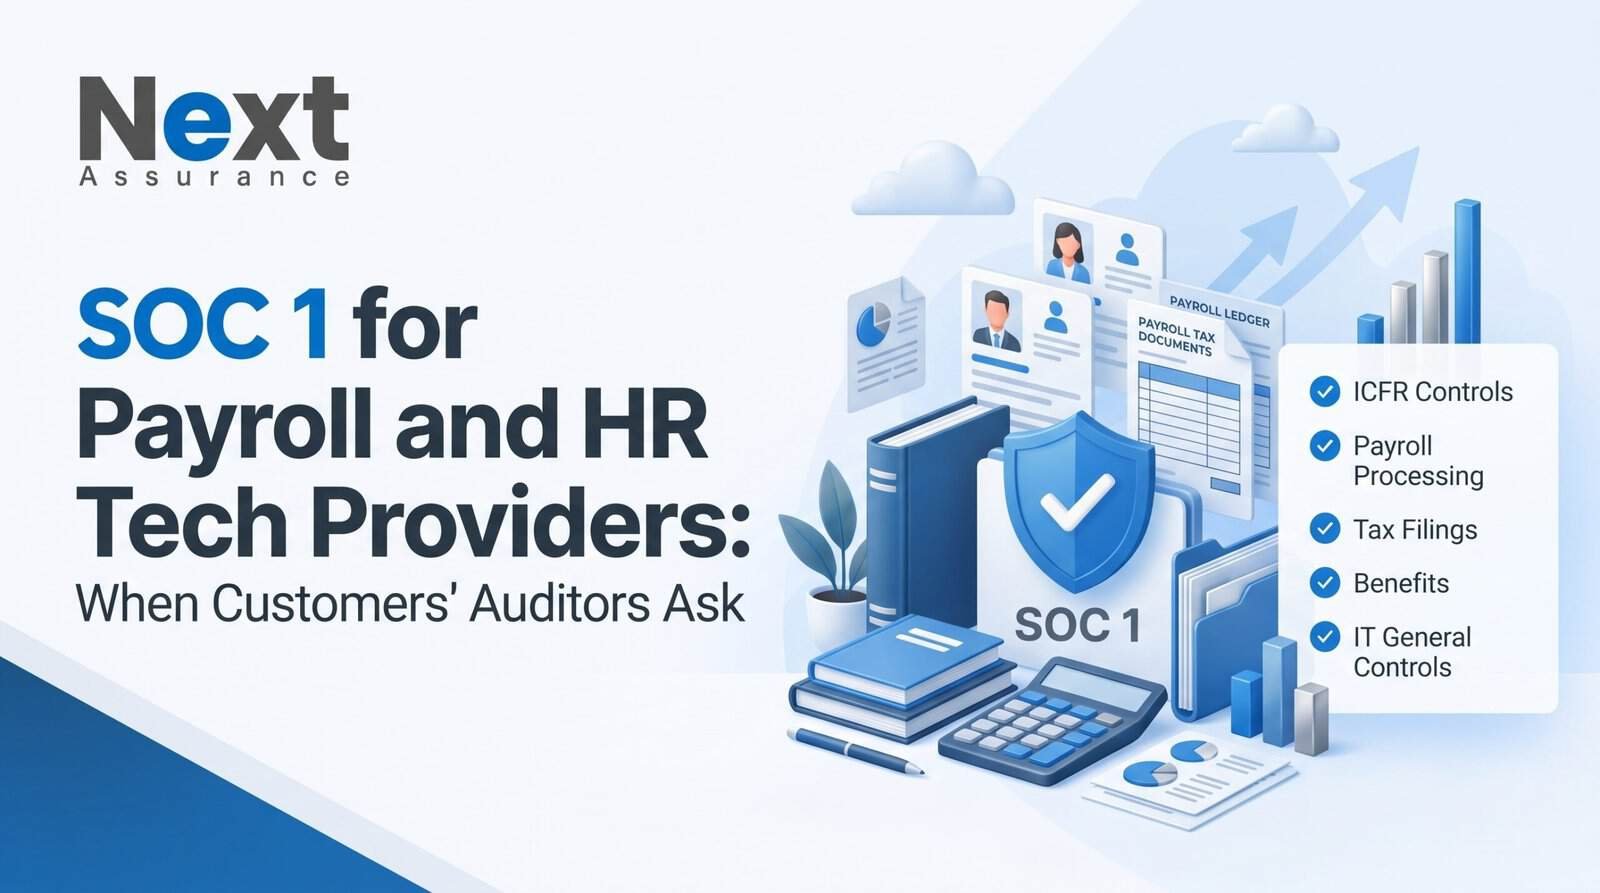
SOC 1 for payroll providers is a CPA report on the controls that matter to your customers’ financial statements, and customers’ auditors often request it because payroll results flow into the books. It is different from SOC 2, which focuses on data security and related criteria.
What is SOC 1 and who reads it?
A SOC 1 report presents the results of an examination of controls at a service organization that are likely to be relevant to user entities’ internal control over financial reporting (ICFR). The AICPA says it is meant for user entities and their user auditors.
In plain terms, your customer’s auditor asks: can we rely on this provider’s processing when we audit the customer’s financial statements? A SOC 1 answers with a CPA’s opinion and test results. See our SOC 1 audit guide and SOC 1 service page.
Why do payroll and HR tech providers get asked for SOC 1?
Payroll and related services produce amounts that end up in customers’ ledgers: wages, taxes, benefits and deductions. When a customer’s auditor tests those balances, relying on your controls can be easier than testing them directly.
| Service | Why customers’ auditors may care |
|---|---|
| Payroll calculation and funding | Compensation expense and liabilities appear in financial statements. |
| Tax filings and remittances | Payroll tax balances and compliance flow to the books. |
| Benefits administration | Deductions and employer cost allocations. |
| Time and expense processing | Inputs that drive payroll amounts. |
The AICPA says SOC 1 users evaluate how a service organization’s controls affect user entities’ financial statements, which is why providers that calculate or record those amounts get the request. This reflects common practice rather than a sourced statistic. HR tools that never touch amounts used in financial reporting, such as pure recruiting software, may not need SOC 1 and are more likely to be asked for SOC 2.
SOC 1 vs SOC 2 for payroll and HR tech
SOC 1 addresses controls relevant to financial reporting, while SOC 2 addresses the Trust Services Criteria for security and related areas. Payroll providers often face requests for both, from different people in the customer’s organization.
| Aspect | SOC 1 | SOC 2 |
|---|---|---|
| Question answered | Can we rely on processing for our financial statements? | Is the service secure and well controlled? |
| Main reader | User entity and its user auditor | Security, risk and procurement teams |
| Basis | Control objectives you define about financial reporting | AICPA Trust Services Criteria |
| Typical trigger | Customer’s annual financial audit | Vendor security review |
For the broader comparison, read our SOC 2 audit guide and financial controls and SOC 1.
What controls are typically in a payroll SOC 1?
A payroll SOC 1 describes control objectives about the accuracy, completeness and authorization of processing, plus the IT general controls that support them. These are examples from common practice; each provider defines its own objectives.
- Setup and changes: authorization and review of new clients, pay rules and master-data changes.
- Input and processing: validation of timekeeping and pay inputs, calculation checks and reconciliations.
- Output and funding: review of payroll registers, approval of funding, tax filing controls.
- IT general controls: access, change management and operations of the supporting systems.
- Subservice organizations: banks, tax agencies’ filing agents and cloud hosts, handled by carve-out or inclusive method.
Because the objectives are the provider’s own, describing them clearly is a large part of the work.
What is the difference between a SOC 1 Type 1 and Type 2 report?
A Type 1 report covers whether controls are suitably designed at a point in time, and a Type 2 adds whether they operated effectively over a period. The AICPA publishes the SOC 1 guidance, and customers’ auditors commonly want a period that overlaps the fiscal year under audit.
- First report: some providers start with a Type 1 to show design while the observation period runs.
- Ongoing: annual Type 2 reports keep coverage continuous for customers’ year-end audits.
- Gap periods: a bridge letter from management can cover the time between the report end and a customer’s year end.
Does AI use change anything for an HR tech provider?
It can change what you describe, not which report you need. If your product uses AI in HR decisions, such as screening candidates, note that the EU AI Act classifies employment uses as high-risk and, under the Omnibus reported by the National Law Review, moved those obligations to December 2, 2027. That is a legal question for counsel, separate from SOC 1. Our SOC 2 for AI companies page covers how AI use is described in SOC examinations.
Next Assurance scopes SOC 1 examinations around the control objectives customers' auditors rely on. See our SOC 1 audit service.
Frequently asked questions about SOC 1 for payroll providers
Do payroll providers need SOC 1 or SOC 2?
Often both, for different readers. SOC 1 answers a customer’s financial-statement auditor about processing that affects financial reporting. SOC 2 answers security and risk teams about data protection. Ask customers which they require; the contract or the customer’s auditor usually decides which comes first.
What is a user auditor?
A user auditor is the CPA who audits the financial statements of a user entity, meaning the company that uses your service. The AICPA describes SOC 1 reports as intended for user entities and their user auditors, who use them to evaluate how your controls affect the customer’s financial statements.
Does an HR software company need SOC 1?
Only if its controls are likely relevant to customers’ internal control over financial reporting. A tool that calculates pay or benefits amounts may qualify. A tool for recruiting or performance management usually does not, and customers are more likely to ask for SOC 2 about data security.
Is SOC 1 Type 2 required for payroll?
Nothing requires it by law, but customers’ auditors commonly ask for Type 2 coverage because it tests operation over a period rather than design at a date. Confirm the period they need, usually tied to the customer’s fiscal year, so your report covers it.
How is SOC 1 different from SOC 2?
SOC 1 reports on controls relevant to user entities’ internal control over financial reporting, using control objectives the provider defines. SOC 2 reports against the AICPA Trust Services Criteria for security, availability, processing integrity, confidentiality and privacy. They answer different questions for different readers.
Can SOC 1 be shared publicly?
SOC 1 is generally restricted to the service organization, its customers and their auditors, so it is shared under agreement rather than published. If you want a public trust signal, a SOC 3 is designed for general use, but it covers the Trust Services Criteria, not financial reporting controls.
Sources
Facts checked against the sources below on October 7, 2026. Control examples reflect common practice; each provider defines its own control objectives.
- AICPA & CIMA – SOC 1: reports on controls relevant to user entities’ internal control over financial reporting; user entities and user auditors.
- AICPA & CIMA – System and Organization Controls: SOC Suite of Services: the AICPA’s overview of SOC 1, SOC 2 and SOC 3 reports.
- AICPA & CIMA – Statement on Standards for Attestation Engagements No. 18: the attestation standard that governs SOC examinations.
- National Law Review – EU Digital Omnibus on AI enters into force: new high-risk dates for employment AI.