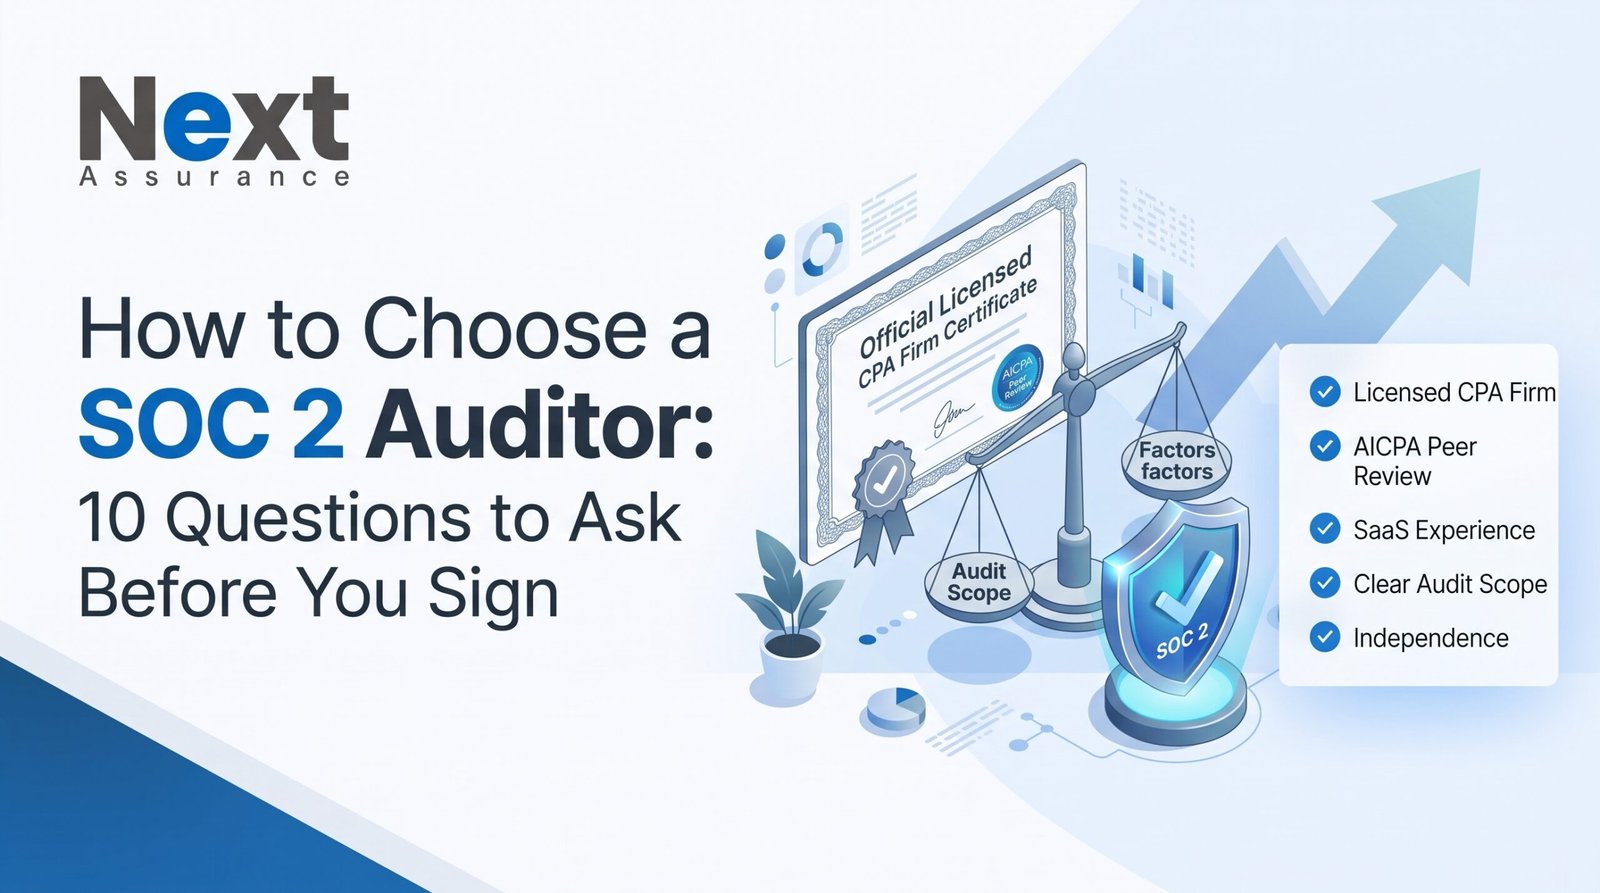
To choose a SOC 2 auditor, confirm that the firm is a licensed CPA firm enrolled in the AICPA Peer Review Program, then compare experience with your type of company, the exact scope and deliverables quoted, and the working relationship, not only the price. Only CPA firms issue SOC 2 reports, so automation platforms and consultants cannot replace the auditor.
Who can perform a SOC 2 audit?
Only a licensed CPA firm can perform a SOC 2 examination and issue the report, because SOC reports are attestation engagements under AICPA standards. Compliance platforms, readiness consultants and security vendors cannot sign a SOC 2 opinion.
SSAE 18, issued by the AICPA Auditing Standards Board, governs how CPA firms perform these engagements. Many companies use a platform to prepare evidence and a separate CPA firm for the examination; our SOC 2 audit guide explains the split. Disclosure: Next Assurance also provides SOC audit services, so compare us with the criteria below as you would any firm.
What is AICPA peer review and why does it matter?
AICPA peer review is the profession’s quality-control check on CPA firms, in which an independent reviewer evaluates a firm’s quality control system or selected engagements. It matters because it is the closest public signal of an audit firm’s quality.
| Review type | Applies to | Possible ratings |
|---|---|---|
| System Review | Firms performing audits, SSAE examinations and similar engagements | Pass; pass with deficiencies; fail |
| Engagement Review | Firms whose highest service level does not require a System Review | Pass; pass with deficiencies; fail |
Per the AICPA’s peer review FAQ, a System Review applies even if a firm performs only one such engagement. Results are confidential, but a reviewed firm may provide its most recently accepted report if asked, and reports can also be obtained from the AICPA Public File in some cases. A firm should not publicize results before the review committee accepts the report.
Which 10 questions should you ask a SOC 2 firm?
Ask questions that test quality, fit and clarity of scope. The answers should be specific, written and consistent across your conversations.
Ten questions for every SOC 2 firm
- Are you a licensed CPA firm, and which CPAs will sign my report?
- May I see your most recent accepted peer review report and rating?
- How many SOC 2 examinations have you completed for companies like mine (size, stack, industry)?
- What do you need from my team, and how many hours should I plan for each phase?
- How do you handle independence if you or an affiliate also provide readiness advice?
- What exactly is in the quote: criteria, systems, report type, observation period, retesting and status meetings?
- Which subservice organizations will be carved out, and how will they be described?
- How do you communicate potential exceptions before the report is drafted?
- What is the typical timeline from kickoff to draft report, and what delays it?
- Can I speak to two recent customers as references?
How do you compare SOC 2 quotes?
You compare SOC 2 quotes by lining up scope, deliverables and assumptions, not just the headline fee. A lower number often means a narrower scope, fewer meetings or more work pushed onto your team.
| Compare | Why it matters |
|---|---|
| Criteria and systems in scope | More categories and systems mean more testing |
| Report type and period | Type II over 3 to 12 months costs more than a Type I |
| Included extras | Retesting, SOC 3 report, bridge letter, status meetings |
| Team and timeline | Who does the work and when fieldwork starts |
| Payment terms | Fixed fee or hourly, and what triggers changes |
Our guide to SOC 2 cost shows published fee ranges and what sits outside the audit fee.
What red flags should you watch for?
The red flags are promises that sound too convenient, such as a guaranteed clean report, a fixed outcome before testing or a firm that cannot show its credentials.
- Guaranteed results: an auditor gives an opinion after testing; no firm can promise one in advance.
- No peer review report: a firm that will not discuss its quality review warrants more questions.
- Vague scope: a quote that does not list criteria, systems and period.
- Same team preparing and signing: ask how independence is managed.
- No SaaS or cloud experience: generalist attest work may not fit your stack.
When should you pick an auditor?
Pick your auditor early, ideally during or right after the readiness assessment, so scope, criteria and the observation window are agreed before you start collecting evidence. That avoids discovering later that evidence will not satisfy the examiner.
See the SOC 2 roadmap for where auditor selection sits on the timeline.
Send us your systems and criteria and we will quote that exact scope, so you can compare it line by line. See our SOC 2 audit service.
Frequently asked questions about choosing a SOC 2 auditor
Who is allowed to issue a SOC 2 report?
Only a licensed CPA firm can perform the examination and issue a SOC 2 report, following AICPA attestation standards such as SSAE 18. Compliance automation platforms and readiness consultants help you prepare, but they cannot sign the opinion. Confirm that the firm itself, not only a partner company, will issue your report.
What is AICPA peer review?
Peer review is the AICPA’s quality-control check on CPA firms, performed by an independent reviewer. A System Review evaluates a firm’s quality control system and applies to firms performing audits and SSAE examinations, with ratings of pass, pass with deficiencies or fail. A firm may share its most recent accepted report if you ask.
Should I choose the cheapest SOC 2 auditor?
Not on price alone. Differences in quotes usually reflect different scope, deliverables or assumptions about how much work your team will do. Compare at least two licensed CPA firms on the same written scope, and weigh peer review standing, SaaS experience and timeline alongside the fee. A cheap quote that omits retesting can cost more later.
Can my SOC 2 auditor also help me prepare?
It depends on the firm’s independence rules and the engagement terms. Some CPA firms provide readiness advice and also perform the examination, while others separate the two. Ask how independence is managed if the same firm advises and audits, and consider using a separate readiness provider if you want a clear separation.
How early should I engage an auditor?
Engage a licensed CPA firm early, ideally during or right after the readiness assessment, so scope, criteria and the observation window are agreed before evidence collection begins. This avoids discovering later that evidence you collected will not satisfy the auditor, and it gives you time to compare more than one quote.
Do I need an auditor with industry experience?
It helps. A firm that has examined companies with a similar stack, such as multi-tenant SaaS on a major cloud, understands your architecture and subservice organizations and can scope more accurately. Ask how many comparable examinations the firm has completed and request two recent customer references before signing.
Sources
Facts checked against primary sources on October 7, 2026.
- Virginia Board of Accountancy – Questions and Answers about the AICPA Peer Review Program: enrollment, System Review versus Engagement Review, ratings, confidentiality and public-file access.
- AICPA & CIMA – Statement on Standards for Attestation Engagements No. 18: the attestation standard that governs how CPA firms perform SOC examinations.
- AICPA & CIMA – System and Organization Controls: SOC Suite of Services: the AICPA’s overview of SOC 1, SOC 2 and SOC 3 reports.